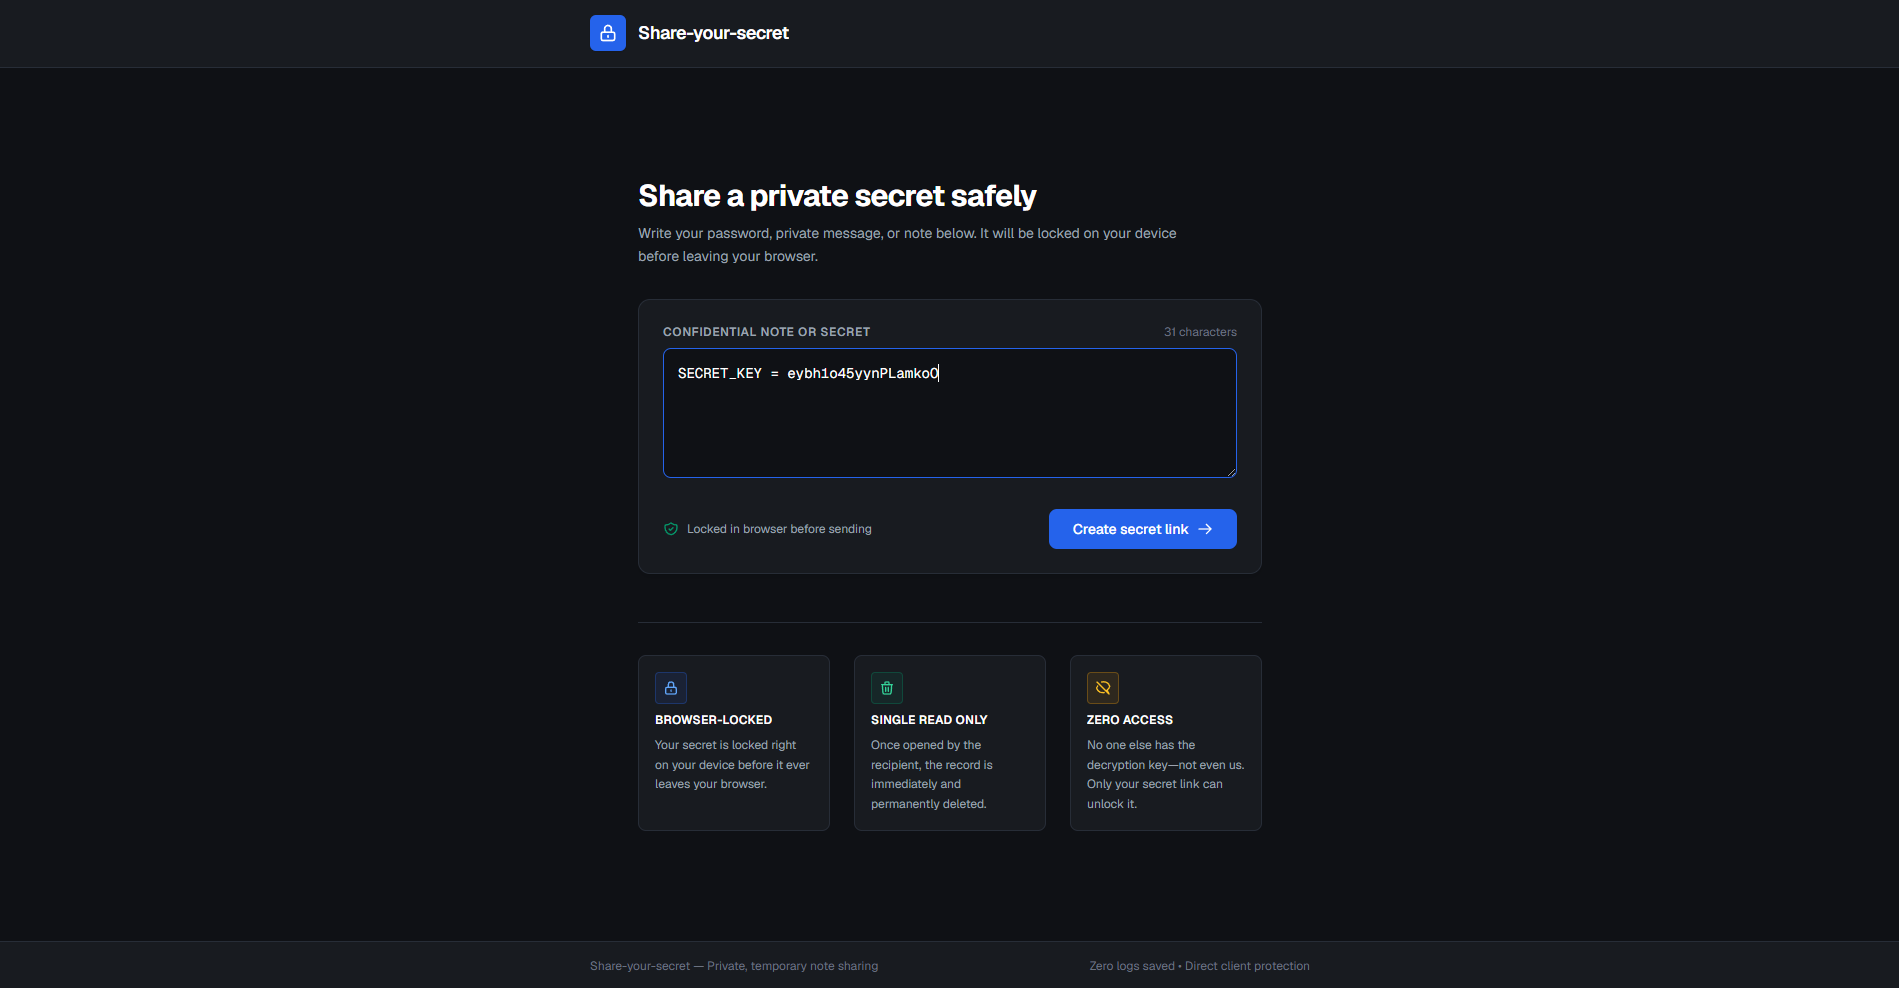
Secret entry and client-side encryption setup
01 / 04Share-Your-Secret
Zero-knowledge secret-sharing web application built on AWS serverless services. Encrypts sensitive credentials in the browser using the Web Crypto API with AES-256-GCM before transport, storing ciphertext in DynamoDB with single-read purge and automated 24-hour TTL expiration.
Architecture pipeline
Browser encryption
Generates an AES-256-GCM key in the browser and encrypts the secret before it leaves the client.
Lambda API
Stores the ciphertext in DynamoDB without ever receiving the decryption key.
Single-read purge
Deletes the record from DynamoDB on the first read request so it cannot be viewed twice.
TTL cleanup
DynamoDB removes unread secrets after 24 hours automatically.
Case study
Sharing credentials and API keys in chat tools leaves plaintext passwords in message logs and search histories.
Encrypts secrets in the browser using the Web Crypto API with AES-GCM before sending them to AWS Lambda. DynamoDB stores the ciphertext, deletes it after the first read, and uses a 24-hour TTL for unread secrets.